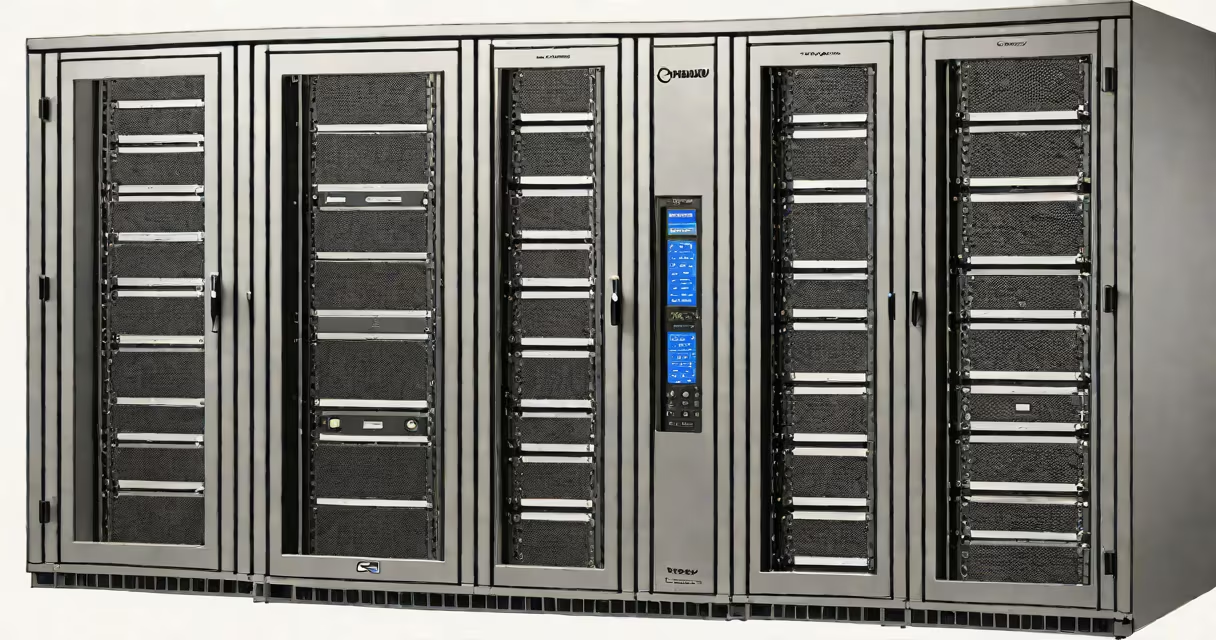
The Orbund Server 4 is a dedicated RADIUS authentication server used to manage secure network access for users and devices in enterprise environments. It verifies credentials, enforces policies, and logs access attempts across wired, wireless, and remote connections.
Deployed in data centers and corporate IT infrastructures, the Orbund Server 4 handles thousands of authentication requests per minute. It supports protocols including RADIUS, Diameter, and LDAP, enabling integration with existing identity management systems such as Active Directory. The device runs a hardened Linux-based OS optimized for low-latency response times and continuous uptime.
Manufactured by Orbund Systems, a company specializing in network access control solutions, the Orbund Server 4 is certified under NIST SP 800-63B for digital identity assurance. It includes built-in support for multi-factor authentication (MFA), time-based one-time passwords (TOTP), and certificate-based authentication using PKI.
The Orbund Server 4 acts as a central gatekeeper between network access points-like Wi-Fi controllers, VPN concentrators, and switch ports-and user identity providers. When a user attempts to connect, their credentials are sent to the Orbund Server 4 via the RADIUS protocol.
The server checks the username and password against a configured directory service. If valid, it returns an acceptance message with authorization attributes-such as VLAN assignment, bandwidth limits, or session timeout settings. If invalid, it sends a rejection with a reason code. All transactions are logged for compliance auditing.
A real-world example: A university deploys the Orbund Server 4 to manage student and staff access to campus Wi-Fi. When a student connects from a dormitory, the access point forwards the login request to the Orbund Server 4. After verifying the student's credentials through the university's LDAP system, the server grants access to the academic network segment while restricting access to administrative resources.
The Orbund Server 4 supports multiple authentication methods and policy enforcement mechanisms. It can integrate with external identity providers via SAML or OAuth 2.0, allowing single sign-on (SSO) for web portals and cloud services.
It includes a web-based configuration interface with role-based access control (RBAC). Administrators can define access policies based on user group, time of day, location, or device type. For example, a policy may allow employees to connect from home only during business hours and require MFA for access to finance department resources.
Performance benchmarks show the Orbund Server 4 maintains sub-100ms average response times under 5,000 concurrent sessions. It supports load balancing across redundant instances using heartbeat monitoring and automatic failover. The hardware includes dual 10GbE network ports, ECC memory, and a RAID 1 disk range for data redundancy.
| Feature | Specification |
|---|---|
| Authentication Protocols | RADIUS, Diameter, LDAP, SAML 2.0 |
| Maximum Concurrent Sessions | 10,000 |
| Supported MFA Methods | TOTP, FIDO2, SMS, Email |
| Redundancy Support | Active-active clustering, heartbeat sync |
| Compliance Standards | NIST SP 800-63B, ISO/IEC 27001 |
Some organizations assume the Orbund Server 4 replaces their firewall or endpoint protection system. This is incorrect. The server does not scan traffic for malware or enforce network segmentation. Its sole function is credential validation and policy enforcement at the access layer.
Another misconception is that it operates independently. In practice, it requires integration with a directory service such as Microsoft Active Directory or OpenLDAP. Without a centralized identity store, the Orbund Server 4 cannot verify user accounts or apply group-based policies.
A less obvious point: the Orbund Server 4 does not handle encryption of data in transit. It relies on TLS or IPsec to protect communication between clients and the server. The device itself does not encrypt user passwords-it uses salted hashing and secure storage practices to prevent credential exposure in case of physical access.
Enterprises typically deploy the Orbund Server 4 in a dedicated server room with controlled environmental conditions. Physical access is restricted to authorized IT personnel. Network isolation ensures the server communicates only with trusted access points and directory servers.
I once oversaw the rollout of Orbund Server 4 units across five regional offices. We discovered that inconsistent time synchronization caused authentication failures due to expired tokens. Correcting the NTP configuration across all sites resolved the issue. This highlights the importance of maintaining accurate system clocks across distributed deployments.
Best practices include regular audit log reviews, periodic password policy updates, and disabling unused authentication methods. Organizations should also implement rate limiting to prevent brute-force attacks. The Orbund Server 4 includes built-in tools for generating compliance reports aligned with HIPAA, GDPR, and PCI DSS requirements.
For context, a typical enterprise network uses the Orbund Server 4 alongside a RADIUS proxy server to distribute load across multiple locations. This setup improves reliability and reduces latency for remote users. The proxy forwards requests to the primary Orbund Server 4 instance while caching frequently accessed credentials.
The Orbund Server 4 remains a foundational component in modern network security architectures. It enables secure, auditable access to sensitive systems while supporting large-scale user populations with minimal administrative overhead.